 Discovering Negative-Days with LLM Workflows | Spaceraccoon's Blog
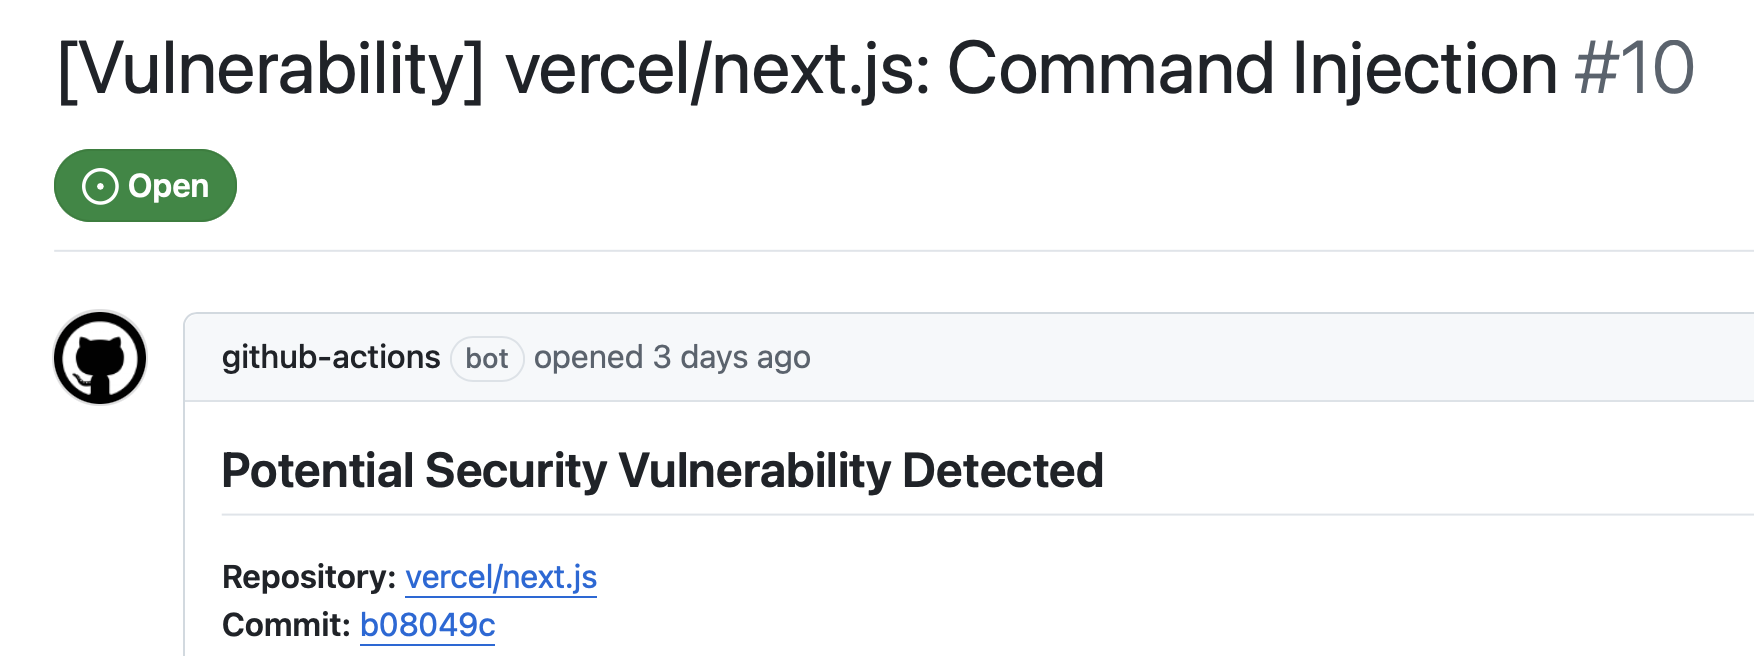
With this little experiment, I validated a critical threat intelligence workflow - we need to be monitoring for open-source vulnerabilities before (or if ever) a CVE is published. Threat actors are 100% already doing this in some form to quickly weaponise and exploit open-source issues. To emphasise the point: This is already happening.